ISO 27001 Readiness for Growing Companies: What to Put in Place First
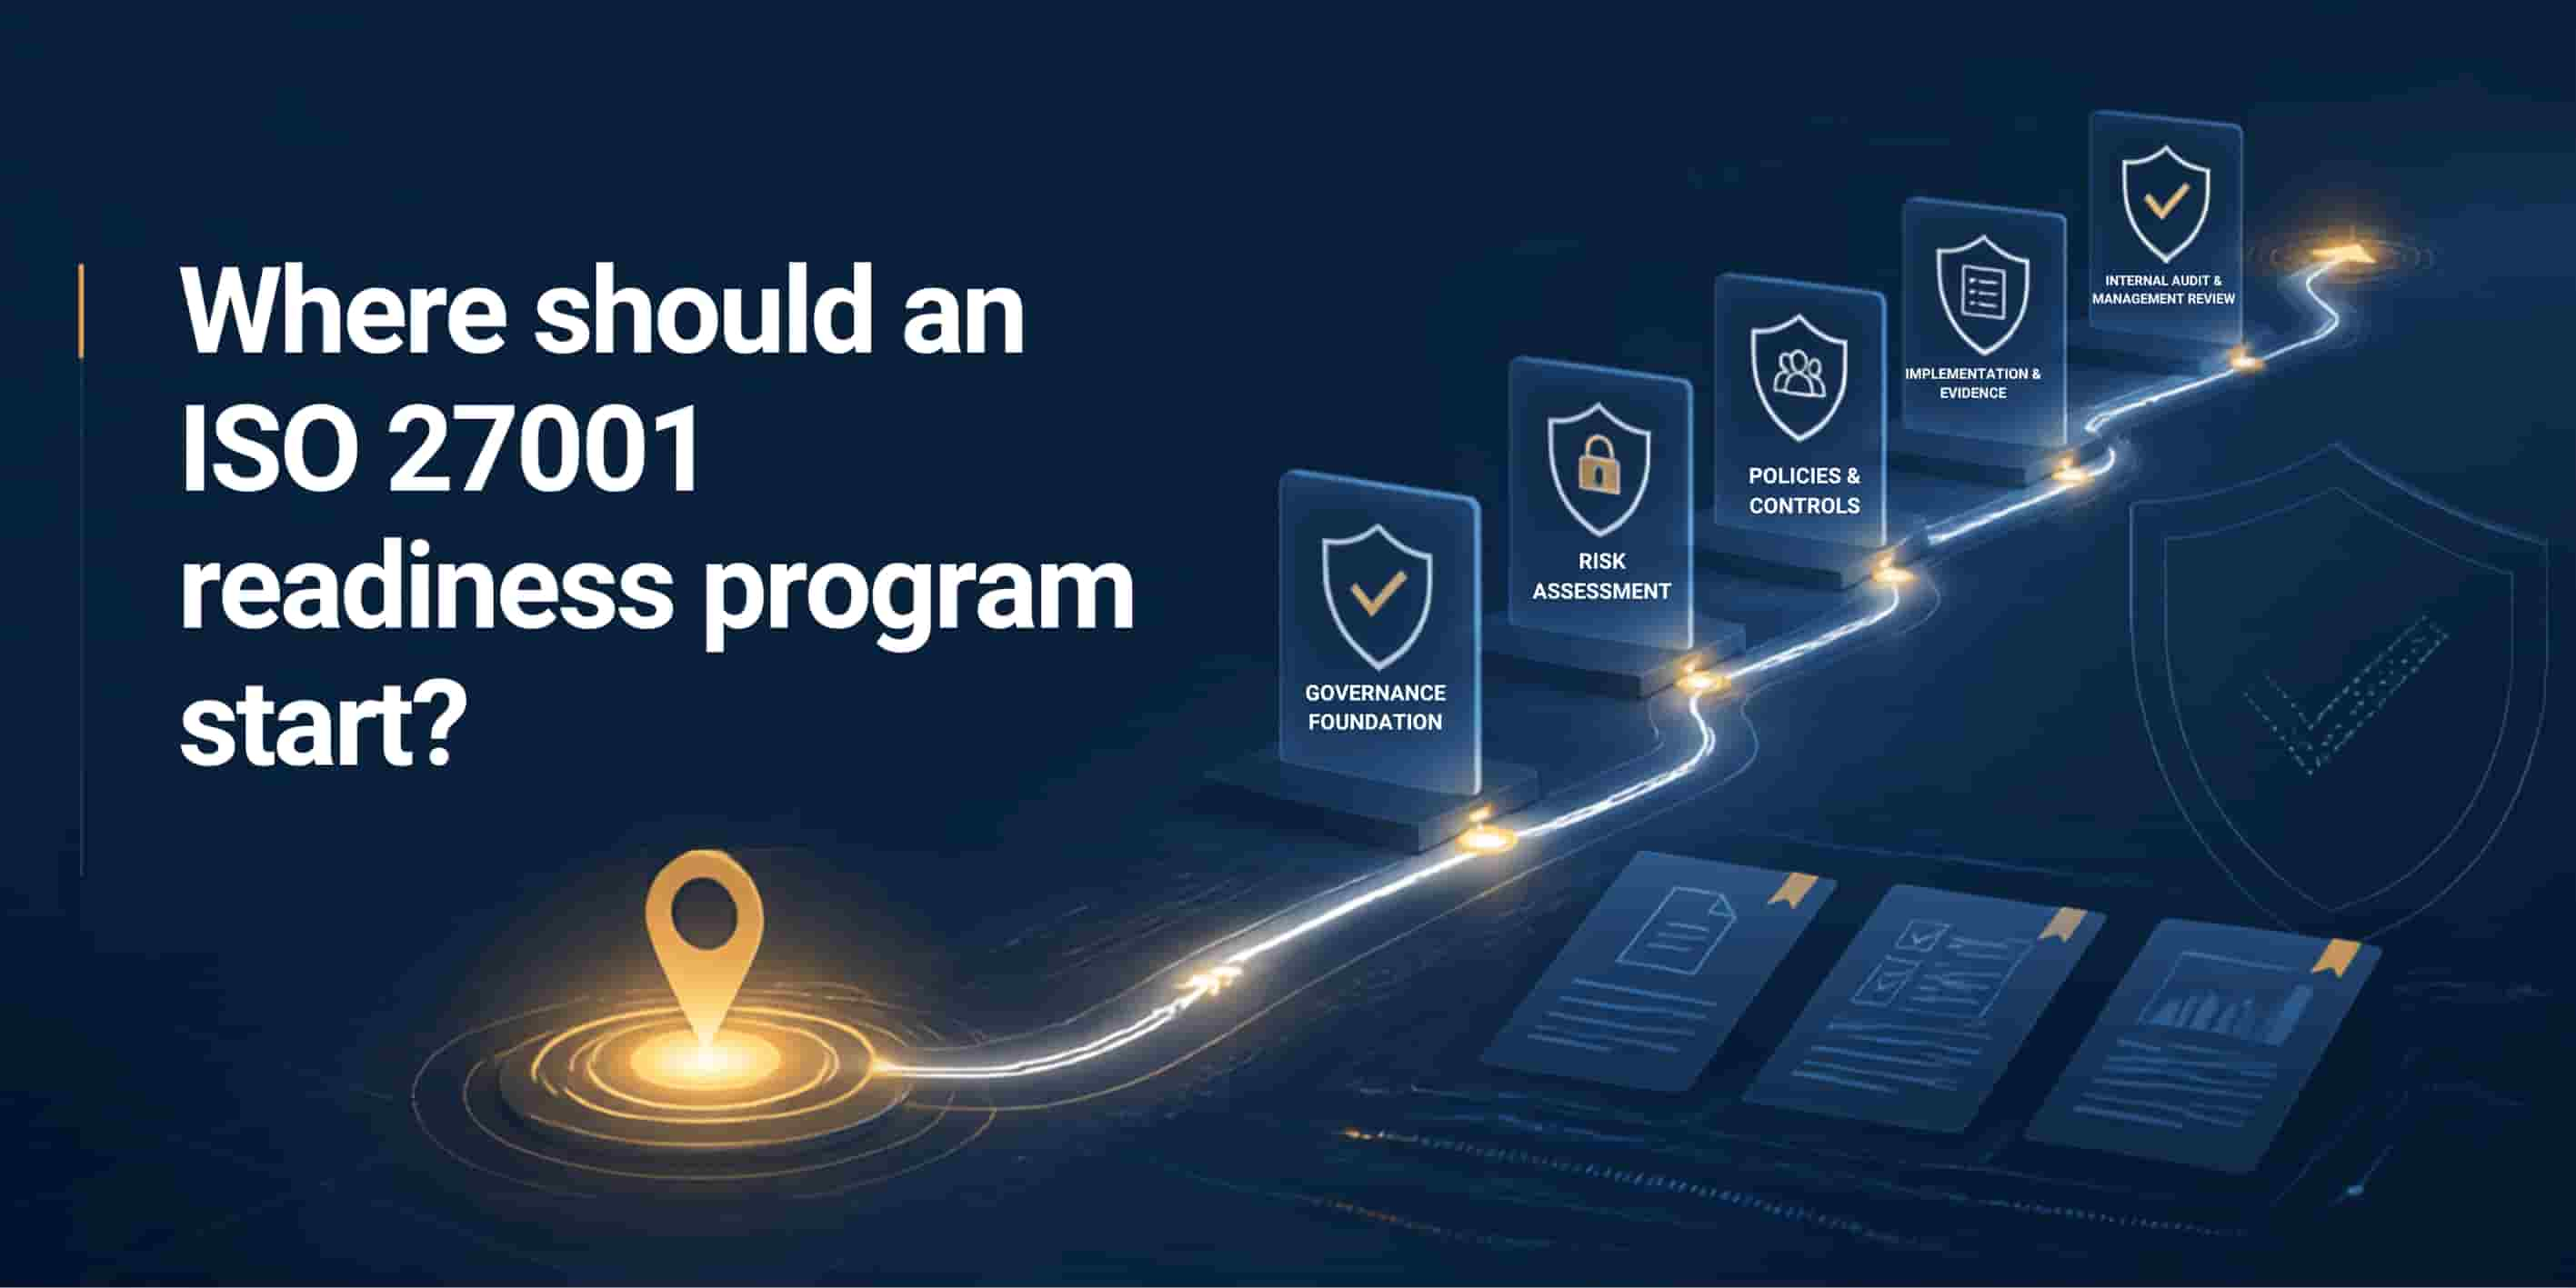
ISO 27001 readiness works best when scope, risk ownership, evidence habits, and operating controls are established before a formal audit timeline begins.
Cybersecurity resources for founders, operators, and finance leaders who need defensible controls without slowing the business down.
Featured in Cybersecurity

ISO 27001 readiness works best when scope, risk ownership, evidence habits, and operating controls are established before a formal audit timeline begins.

A practical sequence for building an ISO 27001 program before the certification clock starts.

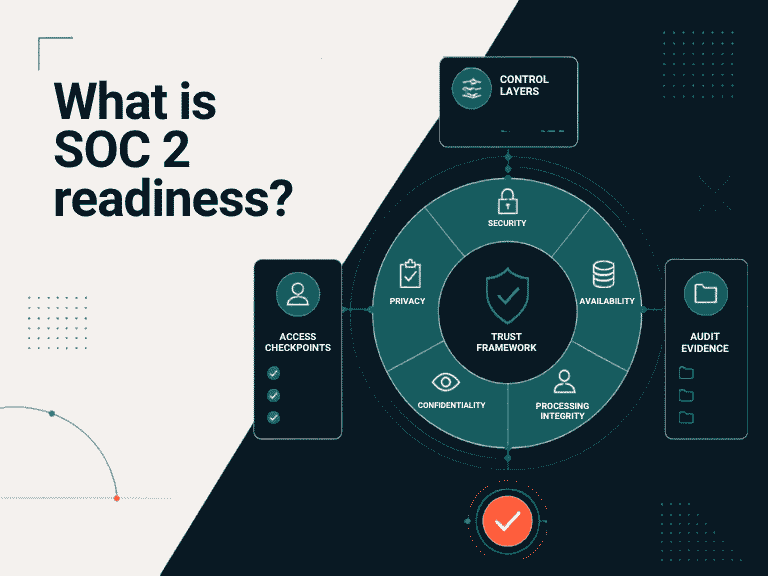
A control-first SOC 2 readiness guide for teams preparing for customer security reviews.

How to know when security leadership is needed before a full-time CISO is justified.

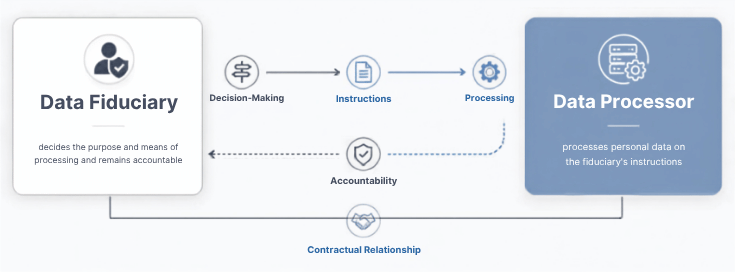
Every vendor contract I have reviewed this year has someone insisting they are "just a processor" the moment DPDPA comes up. Sometimes that is true. Often it is wishful thinking.

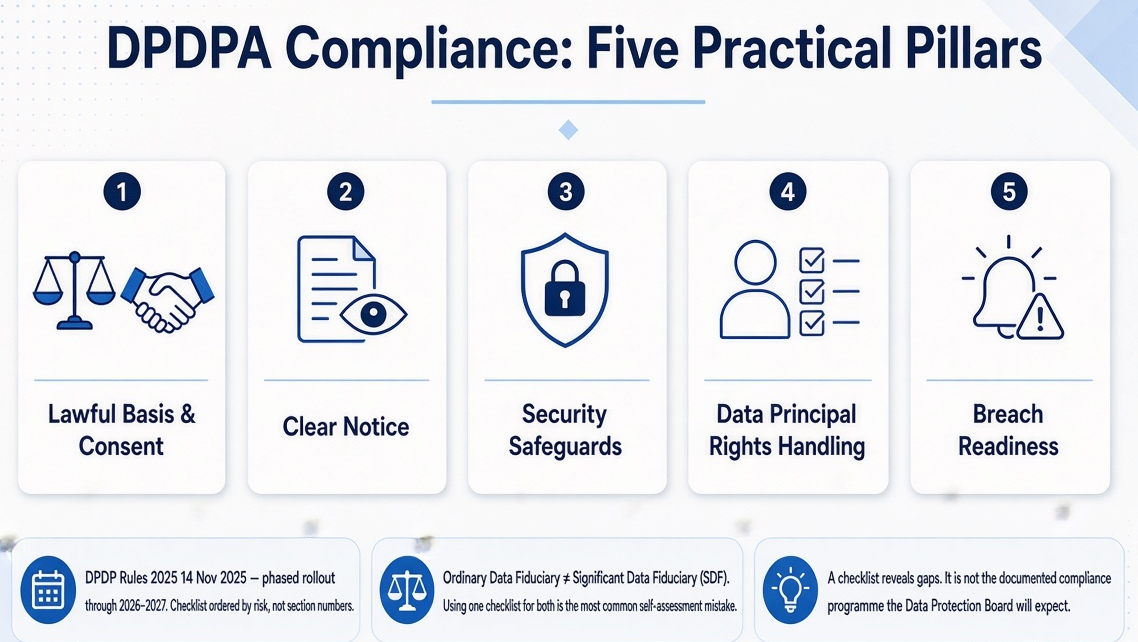
Most "are we DPDPA compliant" conversations I sit in on start with someone printing out the Act and end with nobody sure what to do on Monday morning. Here is the checklist I actually use.
.jpg)
The first time I ran an incident response drill against a 72-hour regulatory clock, the number that scared the room was not seventy-two, it was how much of it we would burn just figuring out what happened.

I nearly wrote this as a ranked "7 best" list with prices attached, until I noticed the source data came mostly from vendors ranking themselves first on their own blogs. Here is the honest version instead.