When a Fractional CISO Makes Sense for a Growing Business
A fractional CISO helps growing companies create a security roadmap, manage compliance, and reduce risk without immediately hiring a full-time executive.
Key Takeaways
- A fractional CISO is useful when security decisions have executive impact.
- Customer audits, compliance programs, and incidents are common triggers.
- The role should produce roadmap clarity, control ownership, and measurable risk reduction.
- Fractional leadership works best when internal owners are assigned.
When does a business need a fractional CISO?
A business needs a fractional CISO when cybersecurity decisions affect revenue, compliance, customer trust, or board-level risk.
Common triggers include enterprise customer due diligence, SOC 2 or ISO 27001 preparation, cloud security concerns, privacy obligations, and incident response planning.
The goal is not to add ceremony. It is to create a security operating model that matches the company's current size and risk.
Stay ahead of security and compliance risk
Get practical cybersecurity, audit readiness, and privacy management insights in your inbox.
What should a fractional CISO do in the first 90 days?
The first 90 days should produce a risk view, control roadmap, evidence plan, and executive reporting cadence.
A good start includes reviewing critical assets, access, vendors, cloud configuration, policies, and existing incidents or near misses.
The output should help leaders decide what to fix now, what to monitor, and what can wait.
How should fractional CISO value be measured?
Measure value through reduced critical risks, faster customer diligence, better audit readiness, and stronger incident preparedness.
Security leadership should create visible progress. Examples include closed high-risk findings, completed access reviews, tested incident plans, and cleaner customer security responses.
Frequently Asked Questions
Is a fractional CISO only for technology companies?
No. Any organization handling sensitive data, regulated processes, or customer security reviews can benefit from security leadership.
Can a fractional CISO manage privacy compliance too?
Often yes, especially where privacy risk overlaps with data security, access controls, breach response, and governance.
Sources & References
Written by
Ankit Manglik
Co-Founder, Cybersecurity and Compliance
Ankit brings 25+ years of experience across GCCs, finance, cybersecurity, internal audit, privacy programs, and enterprise compliance.
View author profileRelated Services
Need security leadership without a full-time hire?
Interakson provides fractional CISO support for strategy, compliance, and operating controls.
Explore Fractional CISO ServicesShare this article
Stay ahead of security and compliance risk
Get practical cybersecurity, audit readiness, and privacy management insights in your inbox.
You may also like
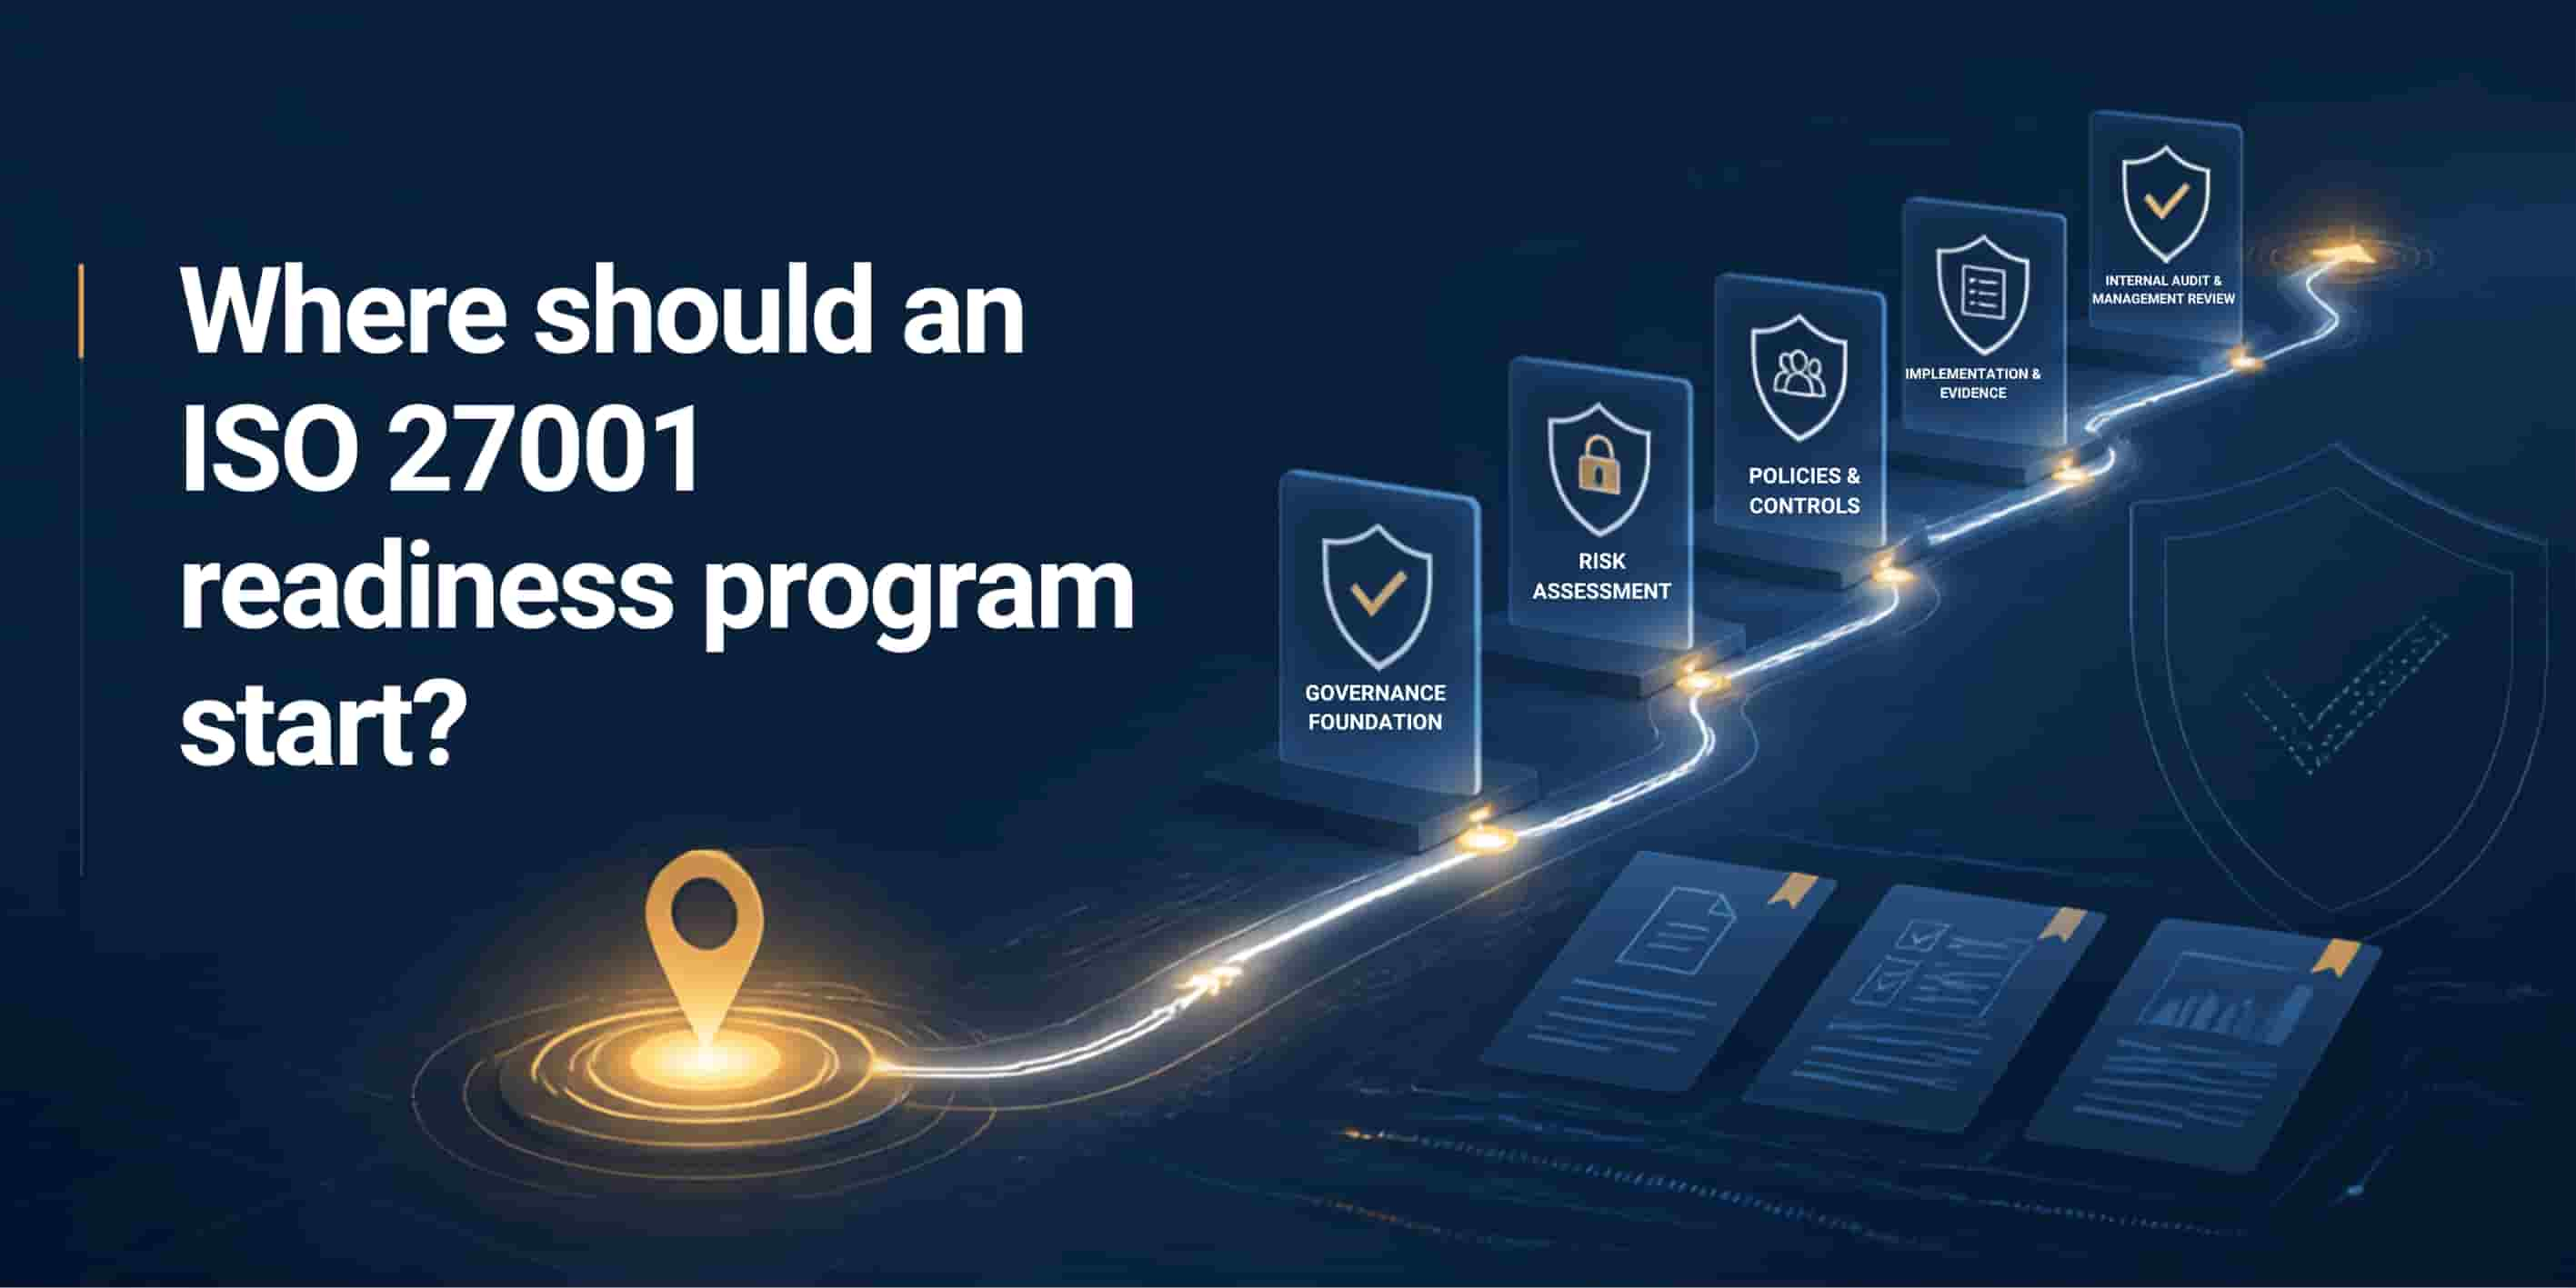
ISO 27001 Readiness for Growing Companies: What to Put in Place First
A practical sequence for building an ISO 27001 program before the certification clock starts.
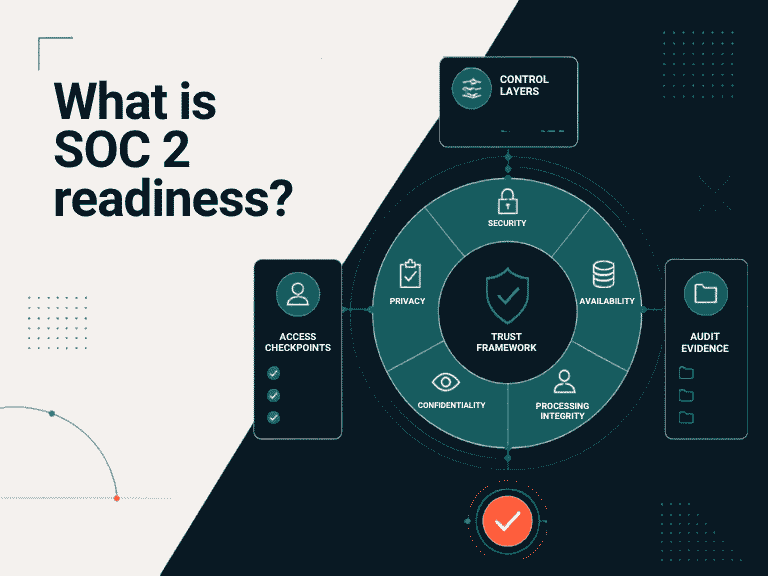
SOC 2 Readiness: The Controls That Matter Before the Auditor Arrives
A control-first SOC 2 readiness guide for teams preparing for customer security reviews.