SOC 2 Readiness: The Controls That Matter Before the Auditor Arrives
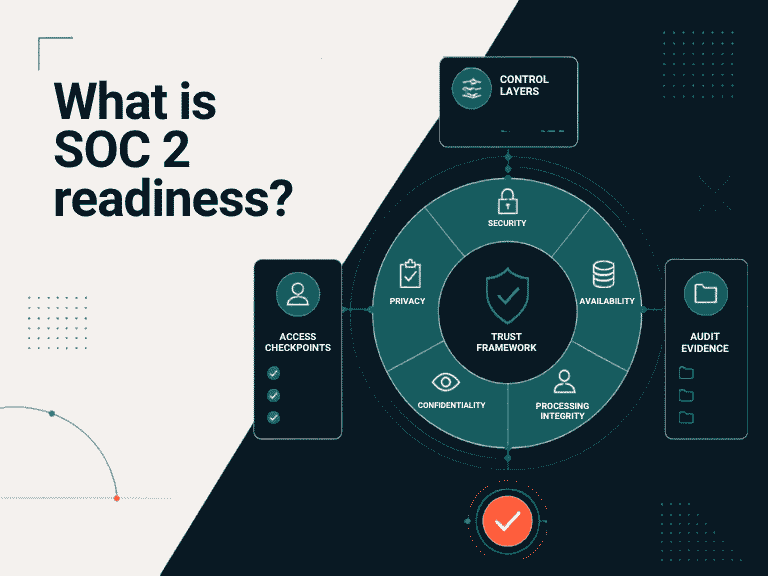
SOC 2 readiness is about proving that important security, availability, and confidentiality controls are designed and operating consistently.
Key Takeaways
- SOC 2 readiness starts with control design and ownership.
- Access, change management, vendors, and incidents usually need early attention.
- Evidence quality matters as much as policy quality.
- Readiness work should support customer trust, not only audit completion.
What is SOC 2 readiness?
SOC 2 readiness is the work required to make controls clear, owned, documented, and testable before a formal attestation.
Readiness helps teams identify control gaps before an auditor tests them. It also gives sales and customer success teams better answers during vendor security reviews.
A readiness project should produce a control matrix, evidence plan, remediation roadmap, and operating cadence.
Stay ahead of security and compliance risk
Get practical cybersecurity, audit readiness, and privacy management insights in your inbox.
Which SOC 2 controls should be prioritized?
Prioritize logical access, change management, incident response, vendor management, backups, and security monitoring.
These areas often cross teams, tools, and business processes. That makes ownership important.
For each control, decide what happens, who does it, how often it happens, and what evidence proves it happened.
How does SOC 2 readiness help customer diligence?
SOC 2 readiness creates a defensible security story that customers can understand before the final report is available.
Enterprise customers increasingly ask about controls, policies, incidents, data handling, and vendor risk. A readiness program gives teams consistent answers.
The commercial value comes from reducing trust friction while strengthening the actual control environment.
Frequently Asked Questions
Do companies need SOC 2 Type I or Type II first?
Many companies start with Type I to validate control design, then move to Type II to demonstrate operating effectiveness over a period of time.
Can SOC 2 readiness be reused for ISO 27001?
Yes. Many controls overlap, although the frameworks and audit expectations are different.
Sources & References
Written by
Ankit Manglik
Co-Founder, Cybersecurity and Compliance
Ankit brings 25+ years of experience across GCCs, finance, cybersecurity, internal audit, privacy programs, and enterprise compliance.
View author profileRelated Services
Preparing for SOC 2?
Interakson helps define controls, document evidence, and prepare teams for attestation.
Explore SOC Readiness SupportShare this article
Stay ahead of security and compliance risk
Get practical cybersecurity, audit readiness, and privacy management insights in your inbox.
You may also like
ISO 27001 Readiness for Growing Companies: What to Put in Place First
A practical sequence for building an ISO 27001 program before the certification clock starts.
When a Fractional CISO Makes Sense for a Growing Business
How to know when security leadership is needed before a full-time CISO is justified.